GRC & Security
Security controls · risk management · compliance — continuously enforced. Identity, encryption, SIEM, vulnerability management, audit evidence and policy-as-code across ISO 27001, SOC 2, NIST and more.
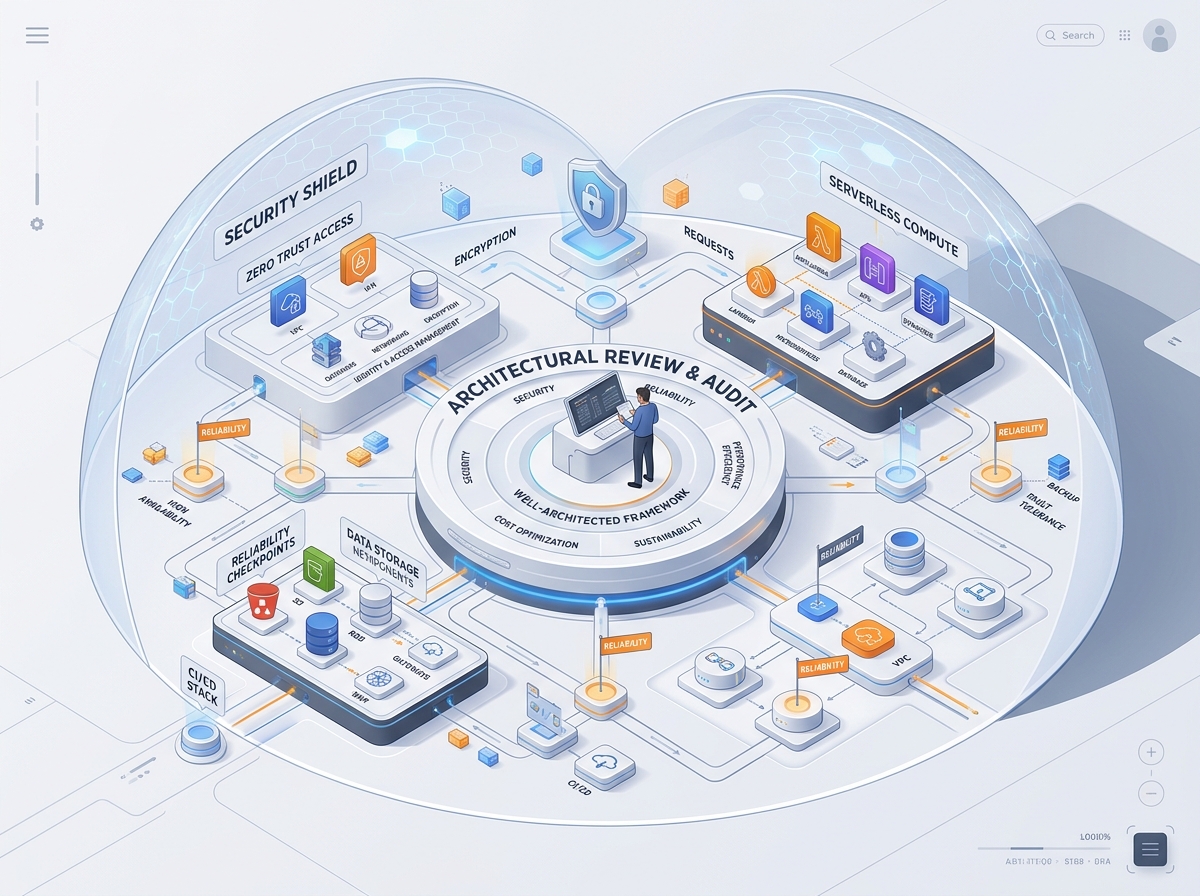
Security Controls
Identity & Access Management
IAM · RBAC · MFA · SSO · Zero-Trust · least-privilege — no implicit trust, every access verified.
Network Security
Firewall · WAF · IDS/IPS · VPN · VLAN · DMZ — layered defences at every network boundary.
Data Protection & Encryption
TLS 1.3 · KMS · HSM · SOPS · encryption at rest — keys managed, rotated and audited automatically.
SIEM & Threat Detection
Log aggregation · anomaly detection · real-time alerting · incident response · forensic readiness.
Vulnerability Management
SAST · DAST · pen testing · CVE tracking · patch management — continuous exposure reduction.
Risk & Compliance
Risk Assessment & Management
Threat modelling · BIA · risk registers · heat maps — quantified, prioritised, tracked.
Compliance Frameworks
ISO 27001 · SOC 2 · NIST · CIS · IEC 62443 · GDPR — automated evidence collection and audit-ready reports.
Audit & Evidence
Immutable WORM logs · tamper-evident audit trails · automated reporting — always audit-ready.
Policy-as-Code
Continuous configuration evaluation · drift detection · automated remediation — compliance never lapses.
Data Governance
Classification · lineage · retention policies · right-to-erase — data handled lawfully at every stage.
Core Deliverables
- Security Posture Assessment Report
- Policy-as-Code Framework — continuous enforcement
- Compliance Evidence Package — ISO 27001 · SOC 2 · NIST
- SIEM & Incident Response Playbook
- Vulnerability Management Programme